We use cookies, including third-party cookies from Google to serve personalized ads through AdSense, to operate this site and understand how it is used. By continuing to browse, you accept this use. See our Privacy Policy and Terms of Use for details, including how to opt out of personalized advertising.
Accept
SmartData CollectiveSmartData Collective
  • Analytics
    AnalyticsShow More
    Flat editorial illustration: The article is about joining public web signals with internal business metrics so BI teams can inter
    Alternative Data in BI: Bringing Public Web Data Into Your Dashboards
    23 Min Read
    Flat editorial illustration: The article is about automating the collection, preparation, and delivery of marketing data across p
    From Data to Dashboards: 5 Marketing Reporting Automation Software Picks
    12 Min Read
    Flat editorial illustration: The article contrasts passive follower totals with a behavioral path from attention and trust to cli
    Creator Analytics Beyond Follower Count: Seven Metrics That Measure Audience Behavior
    11 Min Read
    Flat editorial illustration: The article connects AI and marketing analytics with managerial judgment grounded in consumer behavi
    How an Online MBA in Marketing Connects AI and Data Analytics
    11 Min Read
    What Kind of Problem-Solving Distinguishes Data Analysts From Software Engineers -- AI-generated illustration
    What Kind of Problem-Solving Distinguishes Data Analysts From Software Engineers
    7 Min Read
  • Big Data
  • BI
  • Exclusive
  • IT
  • Marketing
  • Software
Search
© 2008-25 SmartData Collective. All Rights Reserved.
Reading: HIPAA Breach Lessons Learned
Share
Notification
Font ResizerAa
SmartData CollectiveSmartData Collective
Font ResizerAa
Search
  • About
  • Help
  • Privacy
Follow US
© 2008-23 SmartData Collective. All Rights Reserved.
SmartData Collective > Data Management > Best Practices > HIPAA Breach Lessons Learned
Best PracticesBig DataData ManagementInside CompaniesITLocationPolicy and GovernancePrivacySecurity

HIPAA Breach Lessons Learned

onlinetech
onlinetech
5 Min Read
HIPAA Breach Lessons Learned
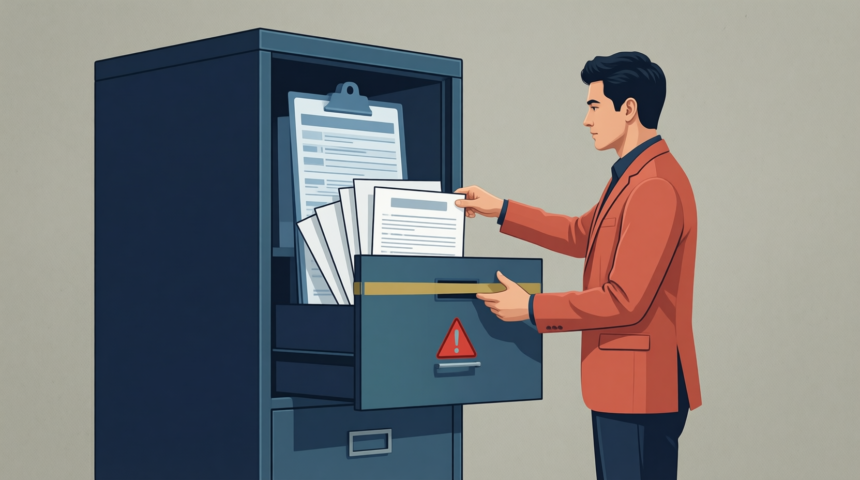
Illustration generated with Qwen Image.
SHARE

While no records were broken when it comes to number of health records disclosed per data breach, the top HIPAA breaches of last year still come with some hard lessons learned about technical and physical security. Learn from their mistakes and protect your healthcare organization from suffering the same fate:

While no records were broken when it comes to number of health records disclosed per data breach, the top HIPAA breaches of last year still come with some hard lessons learned about technical and physical security. Learn from their mistakes and protect your healthcare organization from suffering the same fate:

Who: Crescent Healthcare, a Walgreens company that manages and delivers pharmacy and nursing solutions in alternate site settings.
What: Last December, someone broke into Crescent’s billing center and stole a desktop computer, according to HealthCareITNews.com and the HHS reported breaches data. The desktop computer may have contained names, addresses, phone numbers, Social Security numbers, health insurance data, birthdates and clinical diagnoses. Over 100,000 individuals were affected.
Remediation: The company is retaining employees and service providers on security, and enhancing security policies and procedures.
Lessons Learned: Don’t store ePHI (electronic protected health information) locally on devices. Storing health data in a secure, offsite HIPAA compliant data center with limited, protected access could have prevented this data breach. Check that your HIPAA hosting provider can supply a HIPAA report on compliance to ensure data is safe.

Two-Factor Authentication

More Read
5 Reasons "Data Scientists" are Sexy
5 Reasons “Data Scientists” are Sexy
5 Ways Data Analytics Helps Us Understand the Student Lending Crisis
5 Steps To Launching eCommerce Stores That Are Ready For Big Data
Will Gaming Platforms Adopt AI for Customer Risk Profiling?
How Hospital Security Breaches Devastate Local Communities

Who: Howard University Hospital
What: In early 2012, a former contractor that downloaded patient data (in violation of hospital policy) onto their personal laptop reported the theft of the unencrypted device from their vehicle. Names, addresses, IDs, medical record numbers, birthdates, admission/discharge dates and diagnoses information for over 66,000 patients were all saved locally on the laptop.
Remediation: The hospital extended its policy of encrypting all laptops to include contractor data/laptops.
Lesson Learned: Employee data security policies should cover all employees that have access to ePHI, not just full-time staff. Encrypting data is key. And again, keeping sensitive data off of devices and using a security tool like two-factor authentication for VPN (Virtual Private Network) access cuts down on risk of unauthorized access.

Who: Apria Healthcare, Inc., provider of home medical equipment.
What: Last June, an Apria employee had their laptop stolen from their locked car – billing information for 65,700 patients was stored on the laptop’s hard drive.
Remediation: Apria is working on its internal patient privacy security program and encrypting company laptops.
Lesson Learned: Why do people leave laptops in their cars? Even if locked you’re running a big risk. Aside from that, employee security training may have raised awareness about the dangers of leaving electronics vulnerable, and again, keeping data off of portable devices.

Who: University of Miami Hospital
What: Two employees were accessing patient information from registration ‘face sheets’ and may have sold information to a third party. Face sheets contain name, address, birthdate, insurance policy numbers and the reason for the visit. According to HHS.gov, over 64,000 individuals were affected.
Remediation: The employees were identified and fired.
Lesson Learned: Background checks and employee HIPAA training may have prevented this incident, but often insider threats are the most difficult to detect. File integrity monitoring (FIM) is a service that can be configured and customized to monitor certain folders and files in order to protect ePHI from being altered or destroyed, and fulfills the HIPAA requirement to implement hardware or software to record and examine activity in systems that contain ePHI.

While using the technical services of a HIPAA hosting provider may have prevented or reduced the risk of a data breach in the above top HHS breach cases of 2012, as a covered entity, you need to ensure you can trust your business associates’ security practices. Read Five Questions to Ask Your HIPAA Hosting Provider for a checklist of questions and answers.

References:

Walgreens Company Announces Data Breach
Howard University Laptop Theft Affects 34,000+
Stolen Laptop at Apria Healthcare Exposes Patient Data
University of Miami Hospital Data Incident


TAGGED:cybersecuritydata breachhipaa
Share This Article
Facebook Pinterest LinkedIn
Share

Follow us on Facebook

Latest News

Flat editorial illustration: The article connects downstream report failures, data-quality gaps, and conflicting metric definitio
Signs Your Data Architecture Needs an Outside Review
Big Data Exclusive
Data-Driven Pultrusion: Best GFRP Rebar Machines & ROI
Big Data Exclusive
Flat editorial illustration: The article contrasts tools for gathering fresh interviews with tools for analyzing existing qualita
10 AI Market Research Tools That Turn Qualitative Data into Insights
Artificial Intelligence Big Data Exclusive
Flat editorial illustration: The article compares proxy MCP servers by what an AI agent can do through them: manage proxy account
Proxy MCP Servers: 7 Options and What Each Lets an AI Agent Do
Artificial Intelligence Big Data Data Collection

Stay Connected

1.2KFollowersLike
33.7KFollowersFollow
222FollowersPin

You Might also Like

Tactics to Protect Against Most Common Cyber Attacks
Security

Tactics to Protect Against Most Common Cyber Attacks

9 Min Read
Resources to Protect Personal Privacy and Mobile Security
Uncategorized

Resources to Protect Personal Privacy and Mobile Security

6 Min Read
New Meeting-based Cyberattacks Have Security Specialists on Edge
Data Management

New Meeting-based Cyberattacks Have Security Specialists on Edge

6 Min Read
What Role Does Breach and Attack Simulation Play in Data Protection?
Security

What Role Does Breach and Attack Simulation Play in Data Protection?

7 Min Read

SmartData Collective is one of the largest & trusted community covering technical content about Big Data, BI, Cloud, Analytics, Artificial Intelligence, IoT & more.

How To Get An Award Winning Giveaway Bot
Big Data Chatbots Exclusive
From Bolts to Bots: How AI Is Fortifying the Automotive Industry
Artificial Intelligence

Quick Link

  • About
  • Contact
  • Privacy
Follow US
© 2008-26 SmartData Collective. All Rights Reserved.
Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?